For manufacturers, automotive companies, consumer electronics, SaaS, cross-border commerce and embodied AI businesses. We turn target markets, real data flows and product architecture into regulatory decisions, remediation work, reassessment and defensible evidence — delivered by lawyers and engineers on one team.
Start with the target markets and the actual data flows, then decide which policies, contracts and technical changes are mandatory.
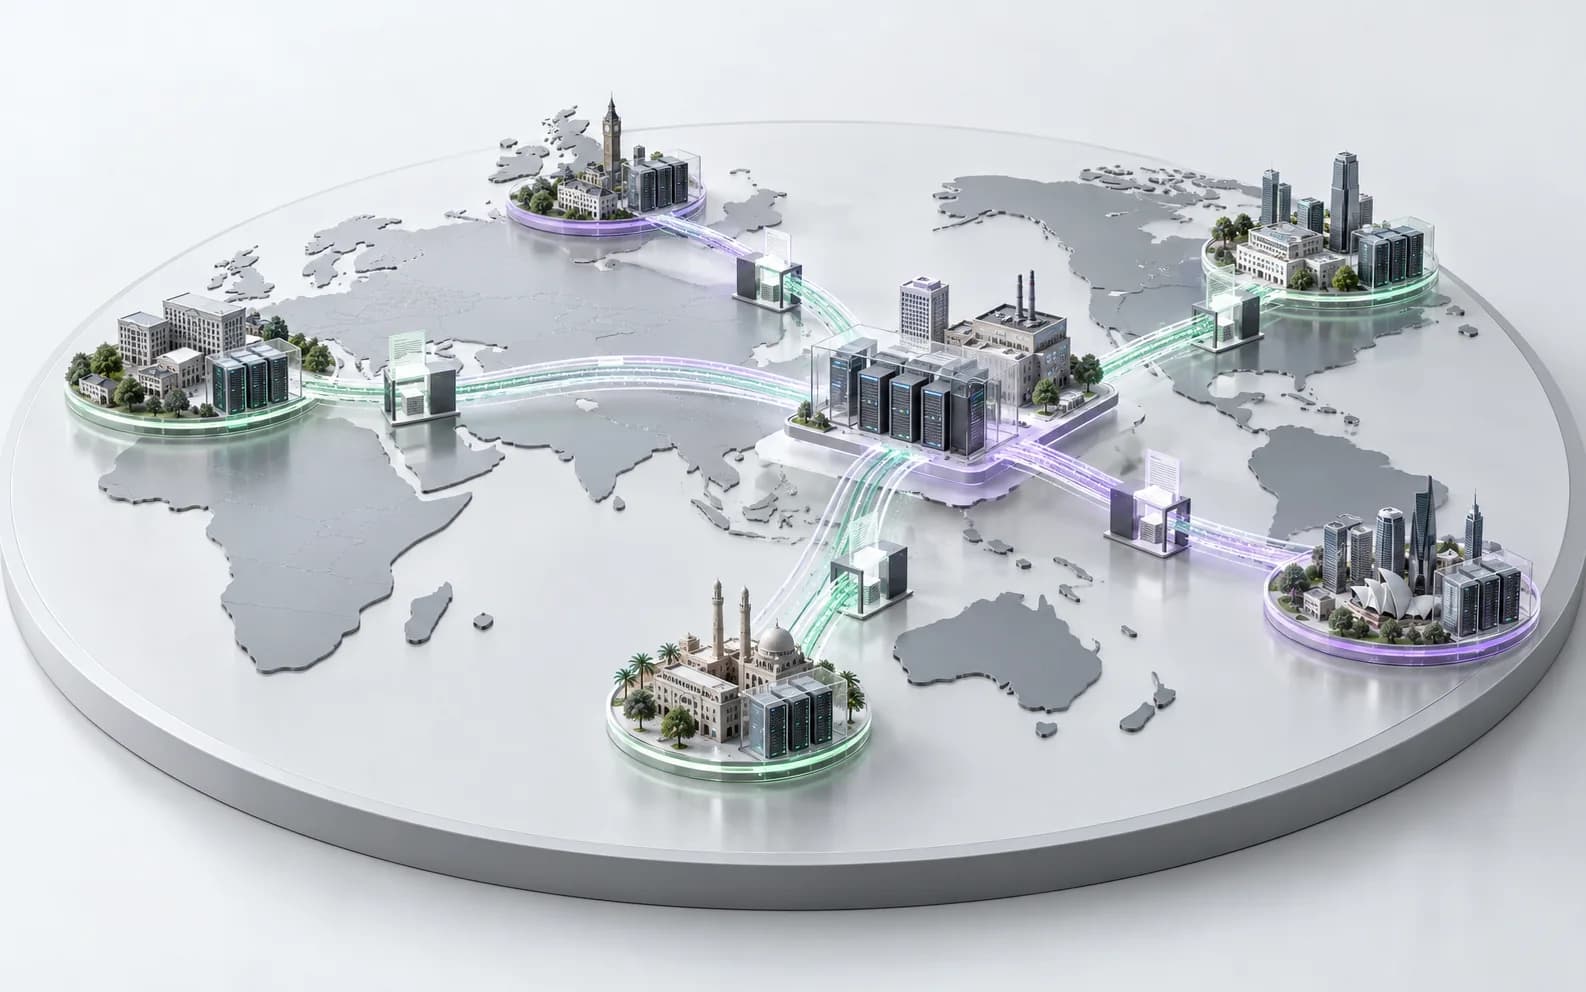
Cross-jurisdiction delivery path
Turn regulatory obligations into decisions across devices, apps, cloud systems, headquarters and suppliers
01
Target markets and applicable laws
02
Cross-border data paths and architecture remediation
03
Contracts, assessments and reassessment evidence
4–6 weeks
One standard compliance project, from discovery interviews to re-assessment with evidence
6+ sectors
Automotive, finance, manufacturing, consumer electronics, aviation and technology distribution
Multi-region
China, EU, UK, US, Asia-Pacific and Middle East compliance scenarios
Legal + Technical
Licensed lawyers and engineers on one team: lawyers can sign, IT can schedule
Consulting services
Different business triggers require different compliance paths. Consulting stands on its own; when remediation needs to become an operating capability, the appropriate product can be added.
When to start now
Your product is heading to the EU, UK, US, Asia-Pacific or Middle East, but applicable rules and actual data flows are not yet clear.
Use-case admission, data sources, model outputs, approval ownership and evidence trails need to be defined before launch.
An inspection, reassessment, data classification or risk remediation program needs owners, milestones and evidence.
EU, UK, US, Asia-Pacific and Middle East coverage, from jurisdiction analysis and data maps to contracts, architecture remediation and reassessment evidence.
AI use-case admission, data provenance, model and output risk, algorithm and generative AI obligations, with executable assessment, approval and audit mechanisms.
For finance, insurance, automotive, energy and public-sector enterprises: risk assessment, classification, PIPL audits, regulatory inspections and remediation loops.
After consulting establishes the path and boundary, add DataAigis AI Agents, DataAigis Data Security & Compliance or DataAigis Privacy & AI Governance as needed to turn project outcomes into continuous operations.
Products
Use consulting to define scope, priorities, and remediation first, then deploy DataAigis AI Agents, Data Security & Compliance, or Privacy & AI Governance as needed. Each product is delivered independently, with no requirement to buy everything at once.
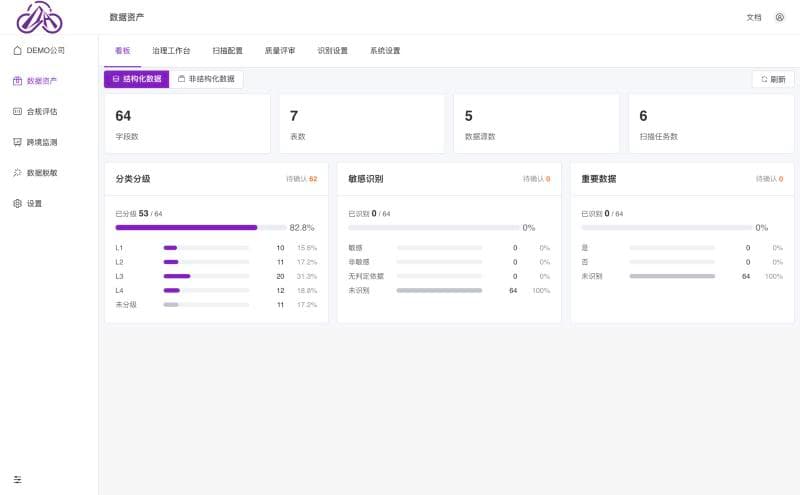
Build runnable, auditable, and scalable enterprise agents and AI applications inside the customer domain.
Four capability centers create a continuous operating loop for enterprise data security and cross-border compliance.
Privacy operations and AI governance on one stack: data subject requests, records of processing and incident response alongside AI assets, risk, compliance and use cases — one register, one audit trail.
Industries and Scenarios
Across market entry, regulatory examinations, data asset governance, and enterprise AI, we put regulation, data, systems, and operating ownership on one delivery map.
Classification, important data identification, risk assessment, remediation loops, regulatory inspection and audit trails.
Vehicle data, user privacy, overseas compliance, supply chain data flows and data security management.
GDPR, US data compliance, cross-border transfer, overseas branches and supply-chain data governance.
Critical business data, industrial data, group-level data assets, supply-chain data and security operations.
Member data, marketing data, cookies/SDKs, user consent, privacy operations and data-use boundaries.
R&D data, clinical data, patient privacy, cross-border collaboration and data access control.
Multi-business, multi-system and multi-region data inventory, classification and governance loops.
Knowledge bases, agents, workflow assistants, permission audits, risk assessment and continuous operations.
Implementation Methodology
Global compliance, domestic data security, and enterprise AI all require business diagnosis, data and knowledge mapping, permission and risk modeling, implementation, and continuous operations. DataAigis delivers them through one consistent project logic.
01
Identify business scenarios, data assets, system boundaries and regulatory constraints.
02
Build risk findings, gap analysis, controls and remediation priorities.
03
Implement policies, workflows, platform capabilities, AI applications and permissions.
04
Run continuous monitoring, evidence retention, reporting and model iteration.
From pilot applications to scaled operations
Business scenario identification
Data and knowledge asset inventory
Permission and risk modeling
AI application and workflow build-out
Effectiveness assessment and safety validation
Continuous operations and audit improvement
ENGAGEMENT MODELS
For current-state assessment, risk evaluation, governance systems, and remediation planning.
Deploy, integrate, configure, and launch DataAigis Data Security & Compliance, DataAigis Privacy & AI Governance, or DataAigis AI Agents for your environment.
Extend from diagnosis and build-out to monitoring, evidence operations, and continuous improvement.
Priority markets and frameworks
We start from target markets, data types, and product architecture, covering China, the EU, UK, US, Brazil, Singapore, and international standards without substituting a generic checklist for applicability analysis.
Supporting tool
Use it to surface possible issues in cookie consent, third-party trackers, privacy notices, and cross-border disclosures. Results are leads for review, not a formal assessment or legal opinion.
Before you decide
Clear answers on project scope, delivery, and purchasing relationships.
We first confirm target markets, product architecture, legal entities, and real data flows, then determine applicable laws and cross-border transfer paths. The first diagnostic should produce priorities, owners, and a remediation route rather than a long list of regulations.
No. Consulting can be purchased independently to complete assessments, policies, and remediation plans. When registers, monitoring, approvals, evidence, or agent capabilities need to become continuous operations, you can add only the relevant product.
Licensed lawyers own legal judgments and signable deliverables. Engineers handle data flows, architecture, and remediation. Trusted agents support scanning, classification, rule matching, report generation, and evidence preparation, with experts reviewing critical conclusions.
Follow the clearest business trigger: start with global data compliance when entering a new market, AI use-case and risk assessment before launching enterprise AI, or domestic data security when facing an examination or unclear data assets. The first discussion should narrow scope, not expand the purchase.
Tell us your target market, business scenario, and data boundaries. We will help determine the first project worth starting.
Book a Project Diagnostic